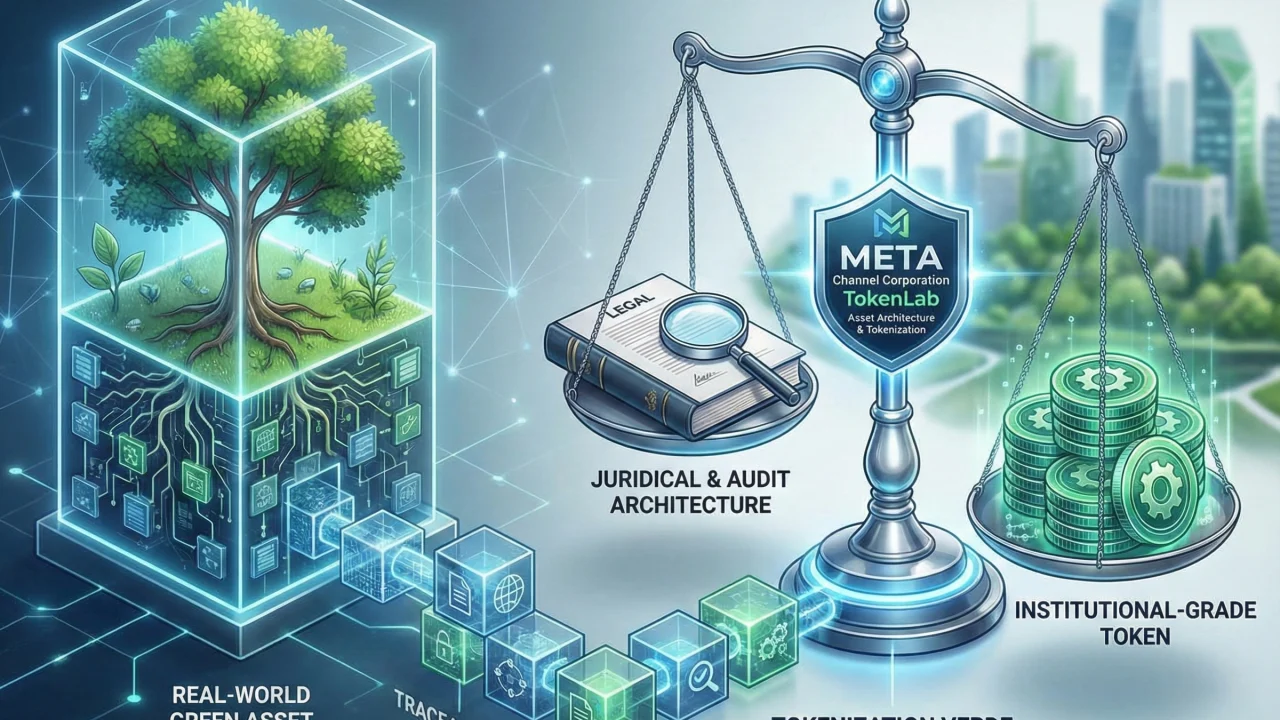
META Channel Corporation | TokenLab – Asset Architecture & Tokenization For years, the debate on tokenisation has been distorted by two opposing caricatures: either it is presented as a technological panacea capable of “fixing” entire markets simply by digitising them, or it is dismissed as a sophisticated form of speculation with a crypto veneer. Both readings are incomplete and, where environmental assets are concerned, dangerously reductive. Tokenisation is not a slogan. It is a technique for representing and transferring rights and, if well designed, a mechanism for raising institutional standards: traceability, auditability, governance, accountability, compatibility with reporting and, above all, defensibility in a real dispute. That is where the decisive nuance lies: in a real dispute. Not in a pitch, not in a white paper, not in a demo. In what happens when the regulator asks questions, when an auditor presses, when an institutional buyer demands guarantees, or when a third party challenges the validity of the environmental attribute being marketed. In “green tokenisation” that nuance is even more demanding, because the aim is to turn a fact in the physical world (a reduction, capture or avoidance of emissions; a renewable attribute; a measurable impact on an ecosystem) into an asset that can be financed, can circulate and can be recognised as a unit of value. That is ambitious. And precisely for that reason it cannot be built on technological naivety. What tokenisation really is (and what it is not) Tokenising is not “putting something on the blockchain”. Tokenising means defining an economic and legal object, giving it a regime for issuance, verification, transfer, restrictions, extinction and challenge, and then representing it through a digital instrument that allows it to circulate under enforceable rules. The token does not create the asset; the token represents the asset. That difference is what separates institutional design from technological theatre. In practice, a token can represent many things: a receivable, a stake, a right of use, a certification, a “claim” to an outcome, or an accounting unit that serves as evidence. With green assets, that ambiguity is precisely where the risk lies: people talk about “tokenised tonnes” as if the token, by its mere existence, were equivalent to a “real” and “reliable” reduction or capture. It is not. Blockchain can guarantee the integrity of the record, time sequencing and resistance to tampering with the history. But on its own it cannot guarantee the truthfulness of what goes into the system. Environmental data comes in through some channel: an auditor, a standard, a measurement methodology, a sensor, a verified report, an official register or an accredited third party. That is where reality lies, and that is where responsibility lies. When this is ignored, a new version of an old problem emerges: greenwashing. Only it is no longer crude greenwashing, but a kind that dresses up something that is not legally watertight as technical infrastructure. Greenwashing does not disappear: it becomes more sophisticated The usual promise is seductive: “every tonne captured will be a unique, traceable token, with no double counting, and the value goes straight to the regenerative project”. It is a good story. But it conflates three different levels. First, “on-chain” uniqueness does not prevent “off-chain” double counting unless there is an exclusivity regime for the environmental attribute and rigorous control of retirements, cancellations, substitutions, subrogations and revalidations. You can have a unique token and, at the same time, a parallel claim in another registry, a duplicate arising from a change of methodology, or a later invalidation of the credit following an audit. The blockchain does not fix that; the legal and governance architecture does. Second, “no intermediaries” is a myth when we are talking about environmental assets with institutional aspirations. There is always significant intermediation: verification, standards, auditing, data custody, certification, supervision, reporting and, in many cases, regulated intermediation. What tokenisation can do is reduce friction and automate processes, but it cannot do away with the chain of trust. With green assets, trust is not a luxury: it is the basis of the asset’s legitimacy. Third, “liquid” does not mean “saleable”. Liquidity is created not by technology but by the market; and the institutional market does not buy tokens, it buys defensible rights. If the asset does not have a clear regime for validity, liability and dispute resolution, the serious market sees it as a risk, not as liquidity. This is where the key idea comes in: tokenisation can be an excellent tool for building integrity, but it can also become a machine for packaging uncertainty. What makes it one or the other is not the chain; it is the design. Green tokenisation: the challenge is not technical, it is institutional Four layers converge in a green asset, and they must be aligned. The first layer is the physical fact or environmental impact: what has been done, where, for how long and with what causal link to the emission or capture. The second layer is technical verification: who measures, using what methodology, under what standard, how often, with what margin of error, with what anti-fraud controls, and what happens if the measurement is revised downwards or invalidated. The third layer is the legal attribution of the environmental attribute: who is entitled to claim it, whether it is transferable, exclusive, temporary or revocable, how double claiming is prevented, and what cancellation or “retirement” mechanisms apply. The fourth layer is the digital instrument: the token, with its logic of issuance, transfer, locking and traceability. If you tokenise from the fourth layer backwards, all you get is an asset that looks “nice” technically but is institutionally fragile. And that fragility is exactly what leads sophisticated buyers to reject it, creates compliance problems and, in the worst case, leads to litigation or penalties for misleading marketing or for defects in the attribution of the right. Green tokenisation done properly is designed from the legal and liability layer, not from the smart contract. That is why there is so much noise and so little real infrastructure: most players come from technology or ESG marketing, not from designing defensible assets. What the institutional market demands (even if it does not say so publicly) The serious market is not looking for “green tokens”. It is looking for mechanisms to finance and circulate climate value with guarantees. It wants to know what it is buying, what it can claim, who is liable, under which jurisdiction, with what audit, under what invalidity regime and with what remedies if the environmental attribute does not hold up. That requires, at the very least, a set of elements that are rarely well resolved: precise legal definitions of the tokenised object; issuance rules linked to verification; a regime for the custody of evidence and evidential traceability; governance of the oracle and the data provider; a conflict-of-interest policy for verifiers; suspension or “freeze” mechanisms where there is suspicion; a cancellation/retirement regime when the attribute is used for claims; and a liability framework that avoids the classic gap of “the DAO is not liable”. In other words, the institutional market requires green tokenisation to be not a technological toy, but infrastructure. TokenLab: tokenising is not “making tokens”; it is building investable assets At TokenLab, within META Channel Corporation, we treat tokenisation for what it is: a results-driven discipline of legal and technical architecture. The question is not “can we tokenise this?”. The question is “can we turn this into a defensible, auditable and financially usable asset without creating a reputational, regulatory or litigation liability?”. With green assets, the standard has to be higher still. Not because the environment is “morally sensitive”, but because the incentives to exaggerate, duplicate or package impact are real, and because regulatory and market scrutiny is growing. The answer is not to refuse to tokenise; it is to do it the way a serious asset is built: with rules, evidence, accountability and correction mechanisms. That is why our approach rests on three non-negotiable principles: evidential traceability, clear legal attribution and enforceable accountability. Without those three pillars, the rest is cosmetic. Evidential traceability means that the system stores not just transactions, but evidence: which environmental event is certified, who certifies it, what methodology is applied, which documents support the event, how the chain of custody of that evidence is preserved and how it is audited. With green assets, the “proof” is not an accessory: it is the asset. Clear legal attribution means that the token does not float around as a vague promise. It must be anchored to a defined right or legal position. Is it a right to use the environmental attribute for a claim? Is it a transfer right with an obligation to retire? Is it a unit of value tied to a conditional outcome? If this is not defined, the token can circulate, yes, but what circulates is ambiguity. Enforceable accountability means that the system has identifiable responsible parties at every link: verifier, issuer, registry operator, evidence custodian, data provider, front-end operator if funds are raised from the public, and a framework of remedies if something goes wrong. A design in which “no one is responsible” is a design that, at the first dispute, collapses or turns toxic. This gap, the recurring “the DAO is not liable”, is not an inevitable consequence of decentralisation, but an architectural failure. In the European context, institutionally sound practice involves anchoring the tokenised asset to an entity with its own legal personality, typically a special purpose vehicle (SPV) or another equivalent structure, which takes on the issuance, the custody of evidence, the duties of truthfulness and liability towards third parties. Serious tokenisation does not eliminate the law or replace it with algorithmic governance: it builds it in from the outset. The token is not the liable party; it is the instrument that represents rights within a structure where there is a real capacity for auditing, supervision, claims and dispute resolution when the environmental attribute is invalidated, challenged or revised. Why “programmable” does not mean “automatically correct” It is often said that the tokenised green asset is “programmable” and can be integrated into DeFi to incentivise sustainable behaviour. In the abstract, that is true. But programming is not the same as legitimising. DeFi does not turn a weak asset into a strong one; it makes it faster, more distributed and potentially riskier. If a green token enters collateral, lending or yield circuits and the environmental attribute is then invalidated, whether because of a methodology error, detected double counting, fraud or a revision of the standard, the problem is not only reputational: it becomes market risk, counterparty risk and legal risk. Programmability amplifies consequences. That is why the design work up front must meet a high standard. There is a lesson here that the market has already learned in other areas: you do not put an asset into financial infrastructure without understanding its validity regime and its liability regime. What is learned through losses in one market may, with green assets, be learned through penalties, litigation and lost credibility. The European framework and the need for regulatory alignment Europe has clearly moved in the right direction: requiring consistency, traceability, disclosure and accountability in green claims and sustainability reporting. The regulatory environment is not designed to “kill” innovation; it is designed to reduce information asymmetry and to stop sustainability from becoming a market in promises with a technical veneer. In practice, this leads to a simple conclusion: green tokenisation that wants to work with serious clients must be able to integrate with compliance, audit, accounting and reporting, rather than live in a parallel universe. That is where many projects fail by design: they build tokens, but not institutional compatibility. And when the sophisticated buyer arrives (a regulated company, a financial institution, a corporation with demanding reporting requirements), it finds that the token “does not fit” its processes or, worse, creates risk for it. TokenLab works precisely to prevent that from happening. It is not about building something “nice” on-chain; it is about making sure the asset survives the real world. The thesis: the token is not the asset; the asset is the architecture Green tokenisation makes sense when it is understood as infrastructure for channelling capital into verifiable projects and for allowing the environmental attribute to be transferred with integrity and under rules. But that sense is lost when it is used as a narrative shortcut: “blockchain = trust” and “token = impact”. The sentence that sums up the right framework is this: tokenisation does not automatically turn an environmental fact into a reliable environmental asset; it merely turns that fact into a tradeable object. From there, whether it adds value or produces sophisticated greenwashing depends on whether the token incorporates a serious regime of verification, legal attribution and accountability. That is what separates an initiative that can scale from one that will, at best, be noise and, at worst, a liability. What “doing it right” means in practice Doing it right means designing the asset first and the token second. It means defining the object with legal precision, anchoring it to verifiable evidence, setting rules for issuance and extinction, putting correction and dispute mechanisms in place, and ensuring compatibility with audit and compliance. It means real governance of data and oracles. It means deciding what can be automated and what must remain under accredited human control. And above all, it means accepting that if the asset is meant to be institutional, it must be prepared for the adverse scenario: inspection, challenge, revision of standards, fraud, error and disputes between parties. That is the standard TokenLab applies. Not because it is more “conservative”, but because it is the only standard that allows green tokenisation to be more than a fad. Closing: value lies not in what you promise, but in what you can stand behind The climate economy needs instruments that make it possible to scale up financing and allocate resources efficiently. Tokenisation can be part of that infrastructure. But credibility is not printed on a token: it is built into the design. At a time when the market already distinguishes between ESG marketing and genuine sustainability architecture, green tokenisation will only have a future in the hands of those who treat it as an institutional discipline, not as a product. That is TokenLab’s positioning: we do not sell narrative, we build defensible assets. And in green tokenisation, that difference is not a matter of aesthetics. It is the difference between contributing to the transition and contributing to the next scandal.
Blockchain and Web3 Finance Corporate Law and Litigation Industry Analysis Innovation and Tech Ecosystems Regulation and Compliance Sustainability and ESG
Green tokenisation: from technology narrative to institutional architecture